https://cheatsheetseries.owasp.org/cheatsheets/HTTP_Headers_Cheat_Sheet.html
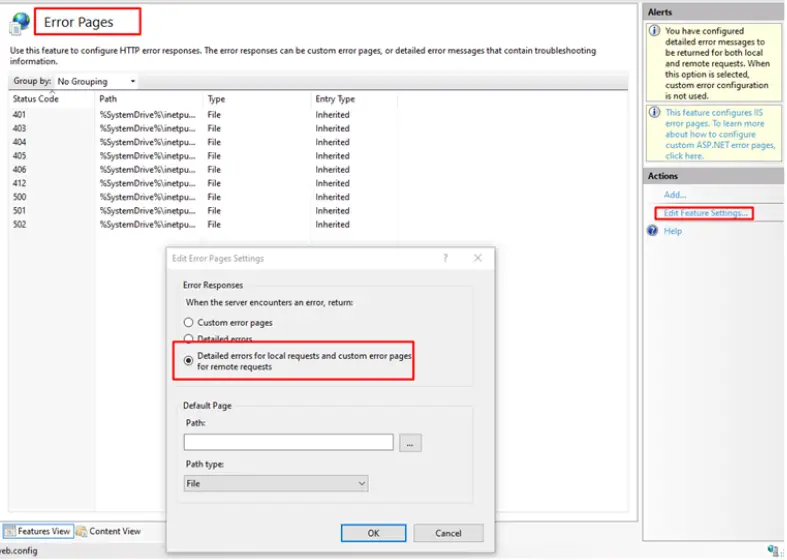
| ASPNET \ Web Server \ Misconfiguration: Missing Error Handling | Disable Detailed errors in IIS | |
| Permissions-Policy | fullscreen=() | |
| Cache-Control | private, no-store | |
| Referrer-Policy | strict-origin-when-cross-origin | we can conclude that the default setting deals with most of the security |
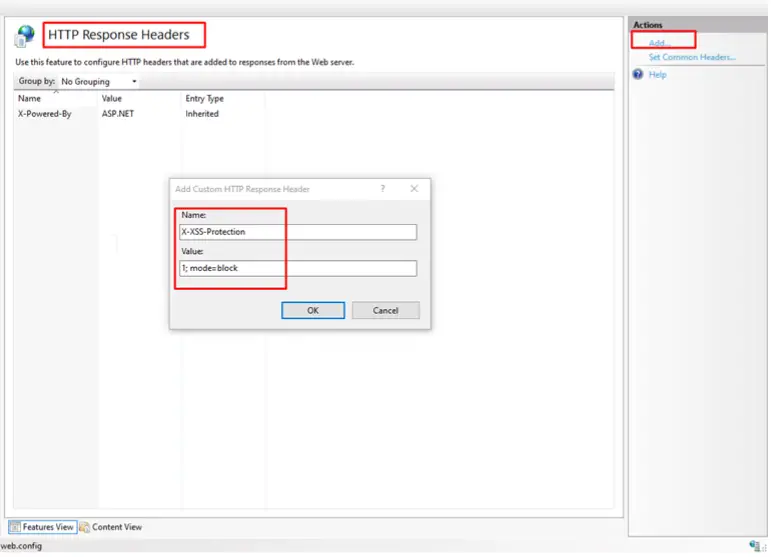
| X-XSS-Protection | 1; mode=block | |
| X-Content-Type-Options | nosniff | |
| Strict-Transport-Security | max-age=31536000; includeSubDomains; preload | HSTS Enable |
| X-Frame-Options | SAMEORIGIN | |
| Content-Security-Policy | default-src ‘none’; script-src ‘self’; connect-src ‘self’; img-src ‘self’; style-src ‘self’; frame-ancestors ‘self’; form-action ‘self’; default-src ‘none’; script-src ‘self’; connect-src ‘self’; img-src ‘self’; style-src ‘self’; frame-ancestors ‘self’; form-action ‘self’; upgrade-insecure-requests | https://content-security-policy.com/ |
| cross-origin-opener-policy | same-origin |